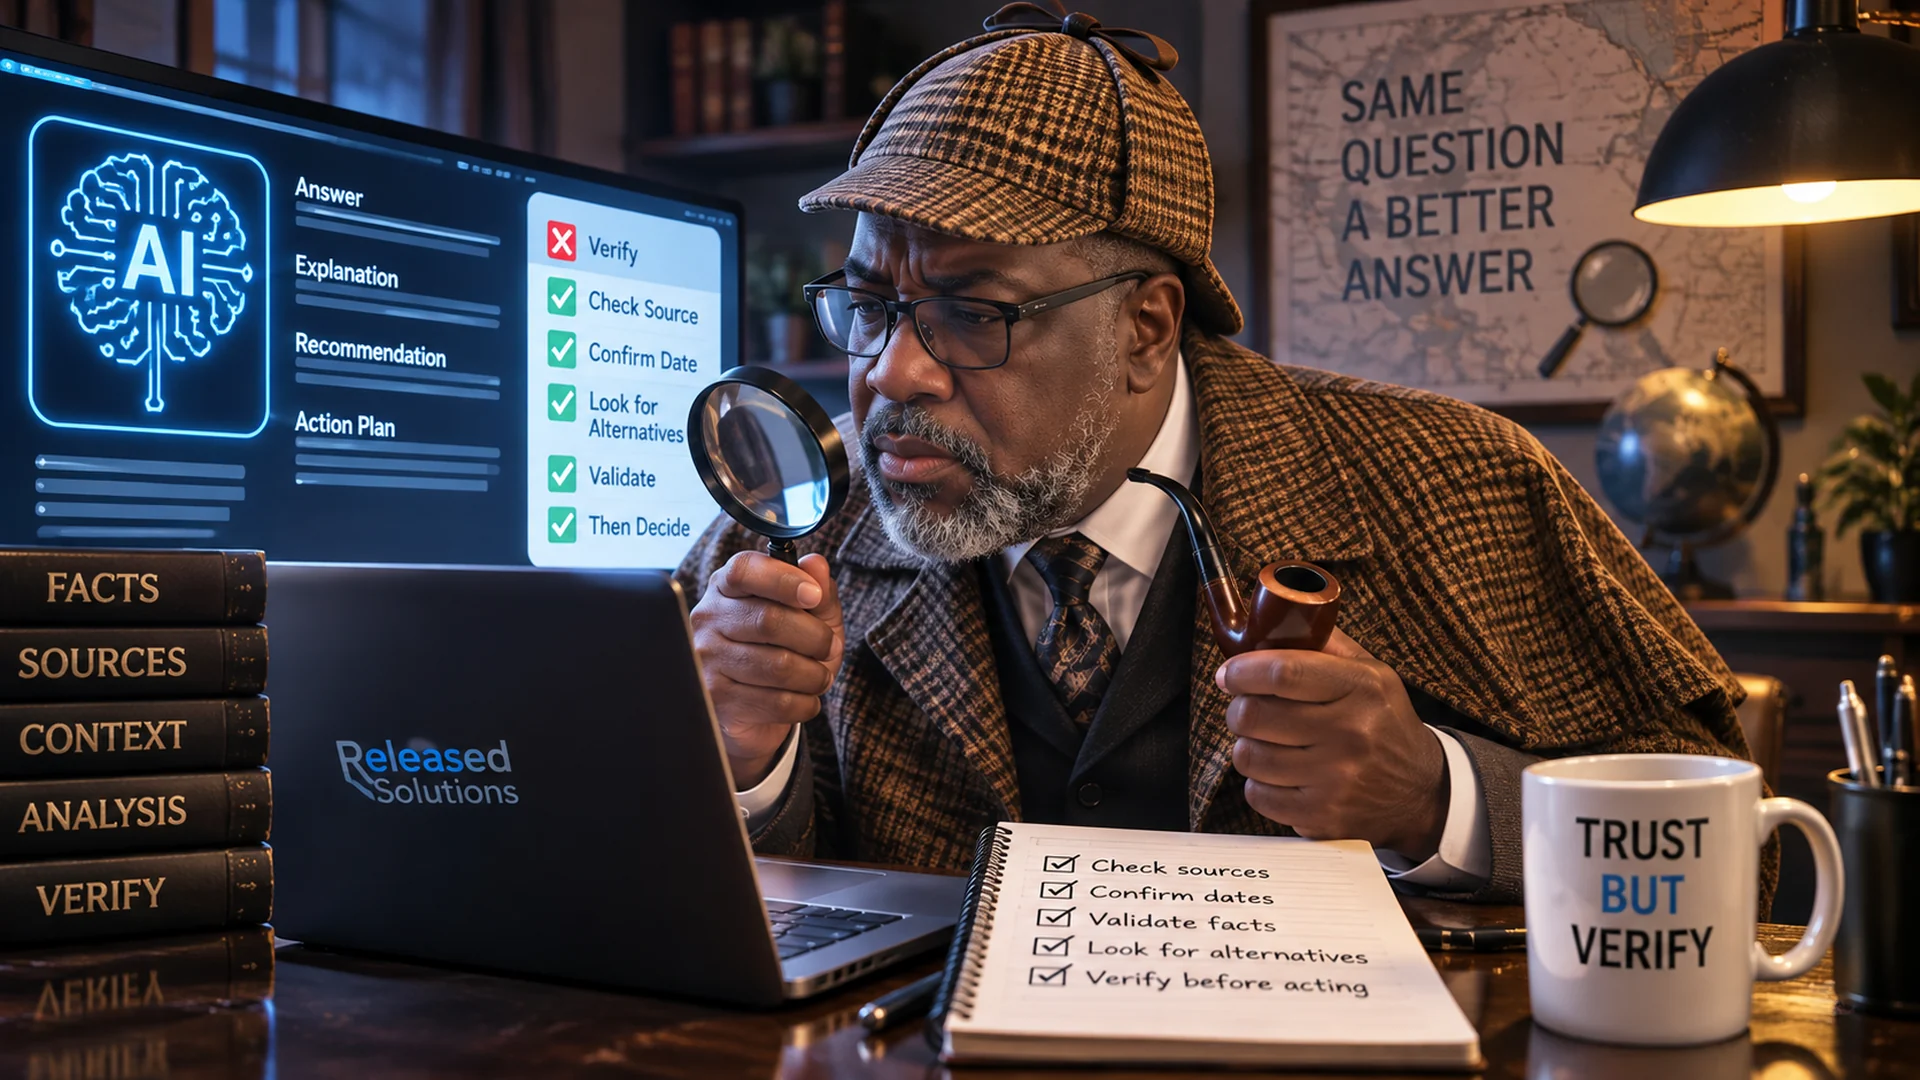

Trust but Verify: How to Use AI Without Blindly Trusting It
I use it to research, write, troubleshoot, analyze, develop websites, work with data, automate processes, and solve problems.
I'm also increasingly allowing AI to do more than simply answer questions. AI can interact with tools, work through multi-step processes, and increasingly take action on our behalf.
I believe that's where we're headed.
But the more responsibility I give AI, the more convinced I become of one principle:
| Trust, but verify. |
|---|
And something that happened to me recently is a perfect example of why.
AI Told Me I Had a Malware Problem
I had several social media posts scheduled to publish automatically through Buffer.
One morning, I received a notification that a post had failed.
I investigated and discovered the problem pretty quickly. My web hosting account had expired. I renewed the account and the website came back.
Simple enough.
Then I asked AI to help me get everything back on schedule.
That's when things got interesting.
The AI reviewed information available to it and connected the current outage to a malware incident that had happened years earlier. It concluded that malware was responsible for the website being unavailable.
That sounded serious. It also sounded plausible. And it was wrong.
The hosting account had simply expired.
Had I blindly accepted the AI's diagnosis, I could have wasted time investigating malware that wasn't there, changed things that didn't need changing, or potentially created an entirely new problem while trying to solve one that didn't exist.
Instead, I verified.
And that experience reinforced something I've been thinking about for a while.
The Dangerous Part Isn't That AI Can Be Wrong
We already know AI can make mistakes.
The more interesting problem is how convincing AI can sound while making them.
NIST uses the term "confabulation" for situations in which generative AI confidently presents erroneous or false information. NIST warns that risk arises when people believe false content and act on it. OpenAI likewise describes hallucinations as plausible but false statements and says they remain a fundamental challenge for large language models, even as systems improve.
An AI response doesn't necessarily arrive looking suspicious. It can be detailed. It can be beautifully written. It can provide a logical explanation. And it can still be wrong.
Sometimes More Context Can Actually Create the Wrong Answer
My hosting incident revealed another problem that I don't think businesses discuss enough.
The AI wasn't necessarily pulling its conclusion out of nowhere. There really had been a malware incident in the past. The information was relevant to my website. It just wasn't relevant to this particular problem.
We're spending enormous amounts of effort giving AI more context: documents, email, previous conversations, CRM records, analytics, databases, project histories and institutional knowledge.
That's incredibly useful. But more context also means more opportunities for AI to connect two things that shouldn't be connected.
Old information can be mistaken for current information. Correlation can become causation. A previous solution can be applied to a completely different problem.
So perhaps the question isn't simply, "Does AI have enough information?" We should also ask, "Is AI using the right information for this particular decision?"
AI Verification Should Match the Consequence
I don't believe every AI response requires a forensic investigation.
If I ask AI for ten headline ideas, I'm probably not going to independently fact-check every suggestion.
But if AI tells me my website contains malware, a client's advertising campaign should be paused, a DNS record should be changed, a customer hasn't paid an invoice, a contract contains a particular requirement, an analytics report shows a specific result, a production database should be modified, or an email should be sent to hundreds of customers, the consequences are different.
My rule is becoming very simple:
The Temptation of Autonomous AI
This becomes even more important as we move toward autonomous and agentic AI.
Businesses understandably want AI that doesn't need to be babysat. Give it a goal. Connect the tools. Let it work.
That's an exciting idea. I want many of those capabilities in my own business. But autonomy shouldn't mean unlimited authority.
OWASP describes "excessive agency" as a risk when AI systems are given excessive functionality, permissions or autonomy. Its guidance recommends minimizing permissions and requiring human approval for high-impact actions.
That aligns closely with the philosophy I'm developing in my own work:
Let it research. Let it organize. Let it draft. Let it analyze. Let it perform repetitive, low-risk tasks.
But decide where the guardrails belong before giving it permission to publish, delete, spend, send, modify or otherwise take an action that could materially affect the business.
The goal shouldn't be eliminating humans from every process. The goal should be eliminating unnecessary human work while preserving human accountability where it matters.
Prompts Can Help AI Verify Itself
There is another practical tool available to us: better prompting.
I've noticed in my own work that explicitly telling AI not to invent information, to verify claims and to acknowledge uncertainty can improve the quality of the response.
But there's an important qualification:
Telling an AI "don't hallucinate" doesn't magically remove hallucinations. What we can do is ask AI to distinguish facts from assumptions, look for contradictory evidence and verify information against available sources.
Challenge Your Own Answer
Review the answer you just gave me. Identify anything you stated as fact that you have not actually verified. Separate verified facts, assumptions and conclusions. Do not fill missing information with guesses.
Verify Against Sources
Verify the important factual claims in your answer using current, authoritative sources. Show me the sources supporting the claims. If you cannot independently verify something, tell me rather than assuming it is true.
Try to Prove Yourself Wrong
Before I act on this recommendation, challenge your conclusion. What alternative explanations could fit the facts? What assumptions are you making? What evidence would change your conclusion?
That third prompt is particularly powerful. Imagine applying it to my hosting problem. Instead of "website down -> old malware history -> malware must be responsible," I want AI considering alternatives: Could the hosting account have expired? Could there be a DNS problem? Could the server be unavailable? Could there be an SSL issue? Could this simply be a billing problem?
Now AI isn't merely defending its first conclusion. We're asking it to challenge that conclusion.
Stop Before Taking Action
Do not make any changes yet. First explain what you believe is happening, what evidence supports that conclusion, what you have verified and what remains uncertain. Tell me what I should independently check before I authorize the action.
That creates a checkpoint between thinking and doing. For consequential business systems, that's a checkpoint worth having.
Challenge Your Own Answer
Verify Against Sources
Try to Prove Yourself Wrong
Stop Before Taking Action
But Sometimes You Need to Get Up and Look
This may be the most important part of the entire article.
You cannot always prompt your way to verification.
If AI tells me my hosting account expired, I can open my hosting account. If it says my website contains malware, I can check the appropriate security tools and logs. If it quotes a contract, I can open the contract. If it reports a conversion number from GA4, I can look at GA4. If it says an invoice hasn't been paid, I can check the actual financial record.
There is a danger in creating this loop:
Ask AI -> Ask AI if AI was correct -> Trust AI
That's not necessarily independent verification.
A better workflow is:
AI checking AI can be an excellent second pass. But sometimes verification requires a human being to go look.
Trust Is Something AI Should Earn
I don't think the answer to AI's imperfections is to stop using AI. Quite the opposite.
I want to use more of it. I want AI connected to more of the systems I use every day. I want it handling more repetitive work. I want it helping me identify problems before I notice them. And I want increasingly capable AI systems helping small businesses accomplish things that previously required far more time, people and money, though capability always carries a real cost worth understanding.
But greater capability deserves better controls.
I don't want AI autonomy based on blind faith. I want earned autonomy.
Start with a task. Measure the results. Check the work. Understand where mistakes happen. Establish the source of truth. Decide which actions require approval. Then gradually increase autonomy where the system has demonstrated that it deserves it.
That's not being afraid of AI. That's responsible implementation.
The Human Still Owns the Outcome
There's one final test I think every business owner should consider.
If AI produces something incorrect and I send it to my customer, whose mistake is it?
Mine.
If AI gives me a false statistic and I publish it on Released Solutions, I can't restore my credibility by saying, "Well, ChatGPT told me that."
If I allow an autonomous system to make a consequential change without appropriate controls, I made the decision to give it that authority.
AI can participate in the work. It can increasingly perform the work. But responsibility for how we deploy it still belongs to us.
And that may be the most important AI skill businesses need to develop. Not prompting. Not automation. Not even knowing which AI model to use.
Because the future isn't going to belong to businesses that blindly trust AI. Nor will it belong to businesses that are afraid to use it.
It will belong to businesses that learn when to trust it, how to verify it and when to take a look for themselves.
Are You Giving AI More Responsibility in Your Business?
Are You Giving AI More Responsibility in Your Business?
AI can save enormous amounts of time, but successful implementation requires more than choosing the right model. Businesses need to decide what AI can access, what it can do autonomously, what needs verification and where human approval belongs. Released Solutions helps small businesses identify practical AI workflows and build the guardrails around them.