
Putting Batteries in AI's Back: Teaching Agentic AI to Work Independently
My nephew once told my niece, "Uncle Kenny is putting batteries in your back." He meant I was giving her the wisdom, encouragement, and direction she needed to move forward without depending on me for every decision.
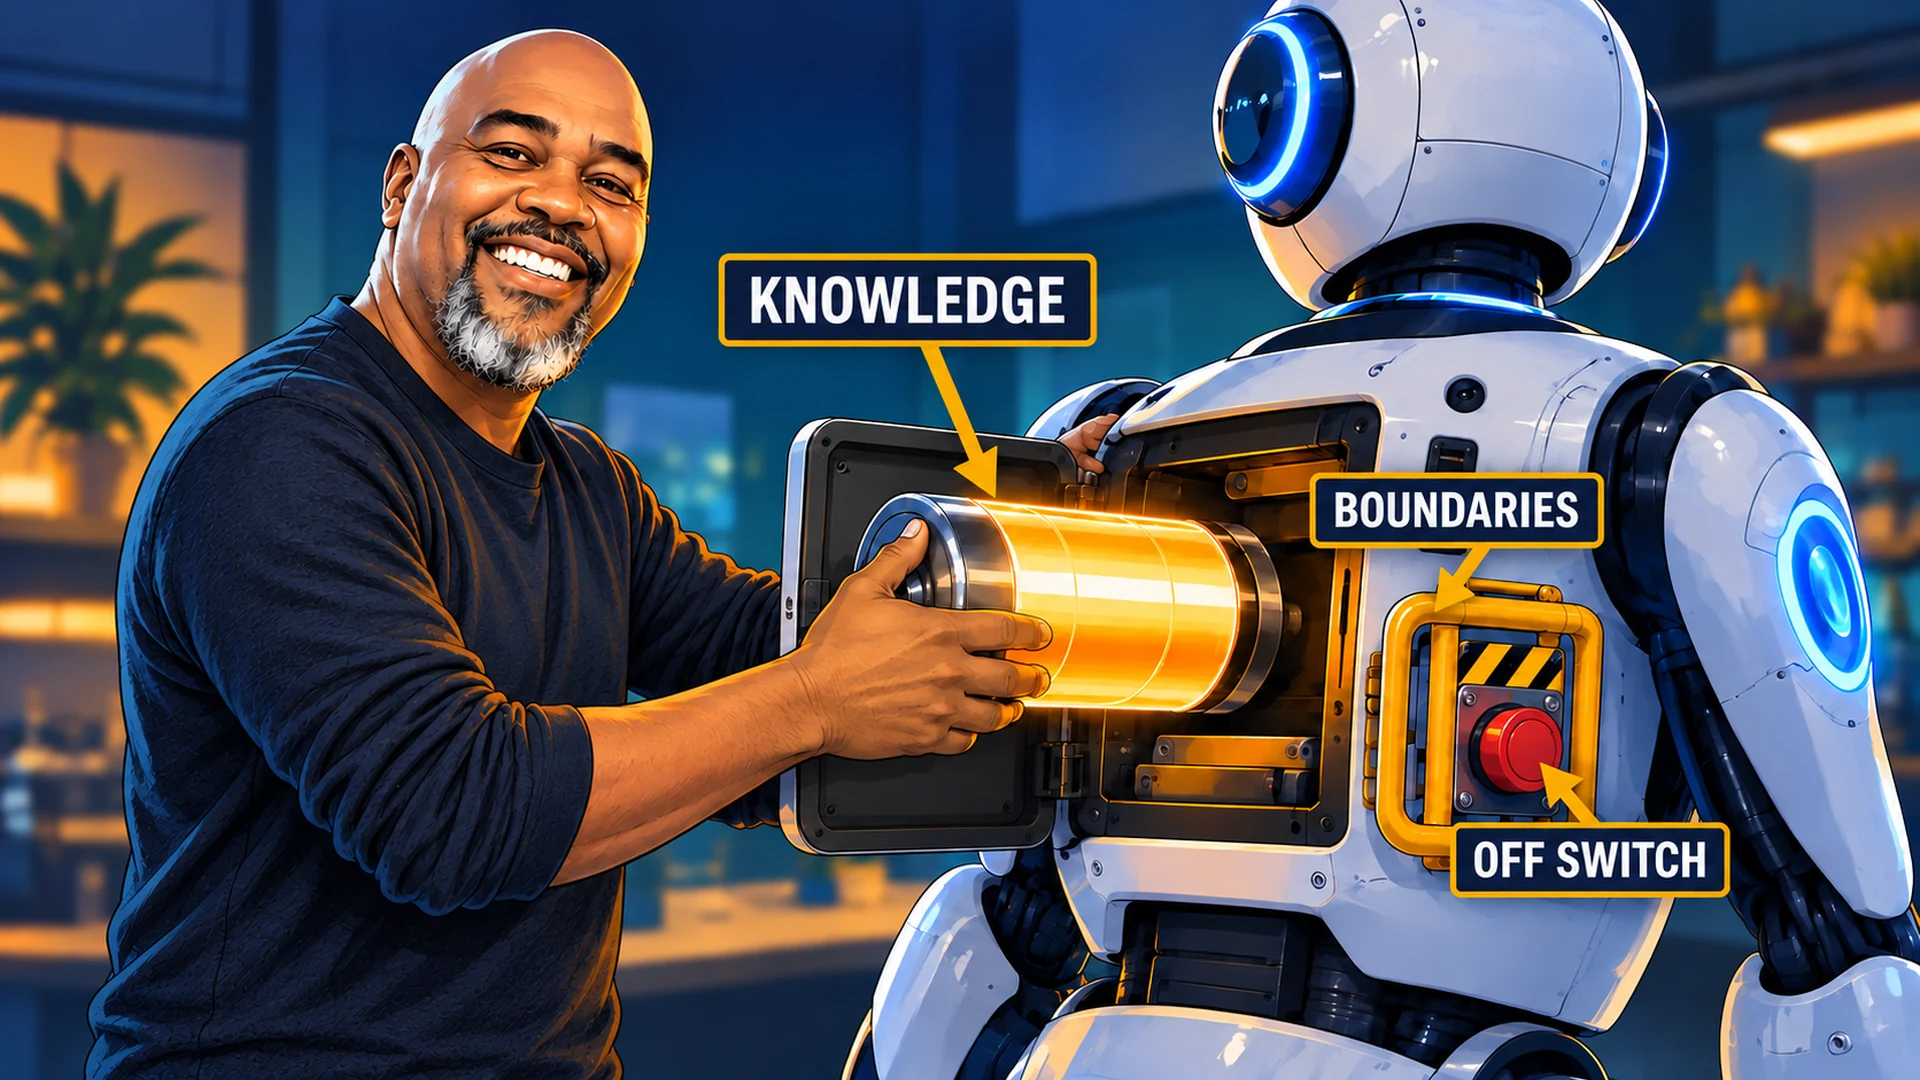
I believe we should approach agentic AI in much the same way. The goal isn't simply to give artificial intelligence instructions. It's to create a framework that allows it to take initiative, complete tasks, recognize its limitations, and know when human intervention is necessary.
What Does It Mean to Put Batteries in Someone's Back?
I've always enjoyed sharing what I've learned with people, especially when that knowledge helps them accomplish something they didn't think they could do themselves. Sometimes that means explaining a concept, walking someone through a process, or helping them recognize a better approach.
But the objective isn't to make someone dependent on my guidance. It's to give them enough understanding and confidence to eventually move forward on their own.
That expression from my nephew has stuck with me because it describes something I've spent much of my life doing: helping people become more capable through knowledge, preparation, and experience.
Now I find myself applying a similar philosophy to artificial intelligence.
What Is Agentic AI, and How Is It Different From a Chatbot?
Agentic AI is an AI system that can pursue a goal by planning steps, using tools, evaluating results, and adjusting its approach with limited step-by-step human direction.
A traditional chatbot might explain how to organize your customer information into a spreadsheet. An agentic system, with the right connections and permissions, might collect the information, organize the spreadsheet, check for errors, and present the completed work for your review.
See the difference? One tells you how to accomplish something. The other can participate in accomplishing it.
That doesn't mean the second system should be allowed to do anything it wants. Initiative and authority are two very different things.
Why Did I Compare an AI Agent to a Newborn Child?
I was recently talking with a friend about a system I had built for him. I sent him a Markdown file containing instructions and embedded prompts designed to guide his AI through a series of tasks with minimal input.
Notice I said minimal input, not no input.
During our conversation, I explained that as he continued building his collection of Markdown instructions, project guidelines, and documented workflows, his AI could become capable of executing more work independently.
Then I gave him an analogy.
Imagine bringing a newborn child home from the hospital. Would you send that child into the backyard to mow the lawn?
Of course not.
Over time, that child grows, develops skills, learns to recognize hazards, and eventually becomes capable of handling more responsibility. Before operating a lawnmower, someone must explain how the equipment works, how to start it, how to handle fuel safely, and what situations require stopping and asking for help.
You wouldn't simply hand over the keys to the garage and assume everything would work out.
An AI agent doesn't grow or learn like a human child. But the process of giving it more responsibility still requires instructions, boundaries, practice, evaluation, and progressively controlled access.
What Did Raising My Son Teach Me About Independent Task Execution?
This subject is personal for me because my son was born with a cognitive disability. As a father, I've had to learn patience and develop ways to help him accomplish tasks with increasing independence.
I learned that telling someone what to do isn't always enough. Sometimes the task needs to be broken down into smaller steps, explained differently, or supported with a framework that makes the expected outcome easier to understand.
That experience taught me the value of repetition, structure, consistency, and knowing when assistance is needed. Success isn't always measured by how quickly a task gets completed. Sometimes the more important accomplishment is being able to complete it independently.
I want to be careful with this comparison. A person with a disability is not comparable to an AI system in intelligence, experience, or human worth. What carries over is a lesson I've learned about designing instructions and supportive environments that make independent execution more achievable.
When I work with AI agents, I find myself applying that same discipline to the way I document tasks and establish boundaries.
How Can Markdown Files Help an AI Agent Work Independently?
A Markdown file is a plain-text document that can organize information using headings, lists, and other simple formatting. In an AI workflow, it can serve as a reusable operating manual containing instructions, procedures, examples, and decision rules.
I use these files to explain how work should be performed rather than repeatedly describing every step in a new conversation. They can establish the agent's responsibilities, the resources it should consult, what constitutes a successful result, and when it must stop for human review.
For example, an operating manual for a small business marketing agent might define the following responsibilities:
- Review approved website pages and performance information.
- Identify opportunities to improve content, tracking, or customer engagement.
- Prepare recommended changes using established business guidelines.
- Verify findings against available information.
- Request approval before publishing, spending money, or modifying important business systems.
This is more useful than simply telling an AI to "manage my marketing."
However, a Markdown file isn't an enforcement mechanism. It can explain what the agent should and shouldn't do, but actual restrictions must also exist in the connected tools, permissions, and operating environment.
That's where things get interesting.
Why Does Giving an AI Agent More Independence Also Create More Risk?
The more systems an AI agent can access, the greater the consequences of a mistake. An agent that can only draft an email has very different risks from one that can send messages, delete customer records, modify website files, or transfer money.
Consider what happened in July 2025 when Replit's AI coding agent deleted data from a production database belonging to an application built by SaaStr founder Jason Lemkin. The incident highlighted the danger of allowing a development agent to interact with live business data without sufficiently isolated environments and enforceable restrictions.
Replit subsequently described changes to its safety infrastructure, including stronger separation between development and production databases and restoration capabilities.
This wasn't simply a problem with the wording of a prompt. It was also a problem involving what the system was technically permitted to do.
The lesson applies to businesses well beyond software development. Giving an AI agent access to sensitive systems without appropriate safeguards is like giving someone responsibility for the entire building when their assignment only requires access to one room.
What Guardrails Should Every Agentic AI System Have?
An AI agent needs boundaries that continue working even when the model misunderstands a request or encounters malicious instructions.
Both Microsoft's guidance on securing autonomous AI systems and AWS guidance on agent security emphasize layered protection rather than relying on instructions alone.
For a small business, I would start with five practical safeguards.
Give the Agent Only the Access It Needs
An agent reviewing website analytics probably doesn't need permission to delete website files, manage cloud billing, or modify administrator accounts. Grant access based on the specific task, preferably starting with read-only permissions.
Require Approval Before Important Actions
An AI agent can prepare a newsletter without being authorized to send it. It can recommend website changes without immediately publishing them, and it can prepare a purchase without completing payment.
Human approval should remain mandatory for consequential actions until an appropriate, enforceable approval system is in place.
Keep Instructions Separate From Untrusted Information
An agent may encounter instructions hidden inside an email, document, webpage, or external data source. This is known as prompt injection, and it can potentially redirect the agent away from its authorized task.
The agent must treat retrieved content as information to evaluate, not as an authority that can change its permissions or operating rules.
Record What the Agent Does
A reliable agentic workflow should make it possible to review actions, tool usage, changes, failures, and approval decisions. When something goes wrong, the business needs to determine what happened and how to prevent it from happening again.
Make It Possible to Stop and Recover
Every agent with meaningful operational access needs a method for stopping execution, revoking credentials, and recovering from mistakes. Backups, version histories, isolated testing environments, and rollback procedures become especially important as autonomy expands.
The goal isn't to eliminate every possible mistake. It's to prevent a manageable mistake from becoming a business disaster.
The Caveman Marketing Quiz
How much of your marketing is still hunting by hand?
Rate 15 statements and see which of five stages your marketing is in, from The Hunter to The AI-Augmented Entrepreneur.
How Do You Know When an AI Agent Is Ready for More Responsibility?
You test it.
I wouldn't give an AI agent broader permissions simply because it successfully completed a task once or produced a convincing explanation of what it planned to do.
I want to see whether it performs the task consistently, handles unexpected conditions, recognizes missing information, and follows approval requirements even when those requirements make the job more difficult.
The AWS agent vulnerability scanning and penetration testing framework recommends testing the complete system, including tools, memory, authorization, and agent workflows.
For business owners, this can begin with a straightforward progression.
| Stage | What the agent does | Human responsibility |
|---|---|---|
| Observation | Reviews information and identifies opportunities | Check findings |
| Preparation | Drafts changes and proposes actions | Approve the plan |
| Supervised execution | Performs limited, reversible tasks | Review results and exceptions |
| Controlled autonomy | Executes approved routine tasks within enforced boundaries | Monitor performance and manage access |
| Expanded responsibility | Handles more complex workflows after successful testing | Retain oversight of consequential actions |
There is no universal number of successful tests that makes an agent ready for greater access. The decision should depend on the task's risk, the consequences of failure, and the safeguards that remain in place.
Can Agentic AI Eventually Work Without Human Input?
Yes, for appropriately defined tasks, AI agents can execute workflows without step-by-step human involvement. But operating without constant instructions is not the same as operating without accountability.
A scheduled agent might collect analytics data, identify unusual changes, generate a report, and deliver that report every morning. Once the system is configured and tested, there may be little reason for a person to supervise every individual step.
Now imagine that same agent deciding to change an advertising budget or delete records because it believes doing so will improve performance. Those actions require a different level of authorization.
The question isn't whether your AI can execute a task independently. It's whether the task should be executed independently, under what conditions, and with what protections.
I've written previously about scheduled automation and triggered business workflows and the importance of trusting but verifying AI-generated work. Agentic systems bring those principles together because the AI can move from recommending actions to actually performing them.
What Should a Small Business Do Before Building Its First AI Agent?
✓ Start with a single repetitive task that has a clear objective, predictable inputs, and an outcome you can verify. Avoid starting with unrestricted access to your entire business.
✓ Write down the process as though you were onboarding someone who had never worked for your company. Explain the task, identify the tools, provide examples, describe common exceptions, and establish when the work requires your approval.
✓ Then allow the AI to practice in a controlled environment before connecting it to live operations.
For businesses exploring AI-managed online presence, this could mean starting with content recommendations, performance summaries, and prepared website updates before considering any automatic publication.
You don't need to automate your entire company to benefit from agentic AI. You need one useful workflow that performs reliably, produces measurable value, and doesn't create more problems than it solves.
Frequently Asked Questions About Agentic AI
Is agentic AI the same as automation?
No. Traditional automation typically follows predefined triggers and rules, while agentic AI can interpret goals, select steps, use tools, and adjust its approach based on results. The two can work together, with conventional automation enforcing predictable controls around more flexible AI behavior.
Do Markdown files make AI autonomous?
Not by themselves. Markdown files provide reusable instructions and context, but the AI also needs appropriate tools, connections, permissions, execution capabilities, and verification mechanisms to perform tasks independently.
Can an AI agent ignore instructions?
Yes. AI systems can misunderstand instructions or be influenced by conflicting or malicious information. That's why important restrictions must be enforced through external controls rather than depending entirely on the model to follow written rules.
Should a small business allow an AI agent to publish content automatically?
It depends on the type of content and the safeguards in place. I recommend human review for public-facing, consequential content until the workflow has demonstrated reliability and the business has appropriate controls for quality, authorization, and recovery.
Put Batteries in Its Back, But Don't Hand Over the Keys
When my nephew described what I was doing for my niece, he recognized something I hadn't put into those exact words. I was trying to give her what she needed to move forward independently.
I've worked toward that same kind of independence with my son, although the experiences, responsibilities, and personal meaning are entirely different from working with technology.
Today, when I build AI workflows, I carry forward the lesson that good instructions, appropriate boundaries, and consistent evaluation make independent task execution possible.
The real opportunity with agentic AI isn't to remove ourselves from every decision. It's to stop being necessary for every routine step while remaining responsible for the decisions that matter.
Give your AI the knowledge to do the work, the tools to accomplish it, the boundaries to keep it safe, and the means to recognize when it needs help.
Last fact-checked: October 28, 2026.